Standards-aligned, not checkbox security
Shaped by the ASD Essential Eight (AU), the NIST Cybersecurity Framework (US) and the principles behind ISO 27001 and GDPR (EU) — used to prioritise, not just to tick a box.
Commonsense services
Security is not an optional add-on. Commonsense helps organisations improve resilience through practical controls, platform configuration, governance and clear risk-based recommendations.
Cyber Security
Our approach draws on the ASD Essential Eight (Australia), the NIST Cybersecurity Framework (United States) and the information-security discipline behind ISO 27001 and GDPR (Europe). We do not stop at the minimum any one of them requires — controls are configured properly, explained in plain English, and followed through.
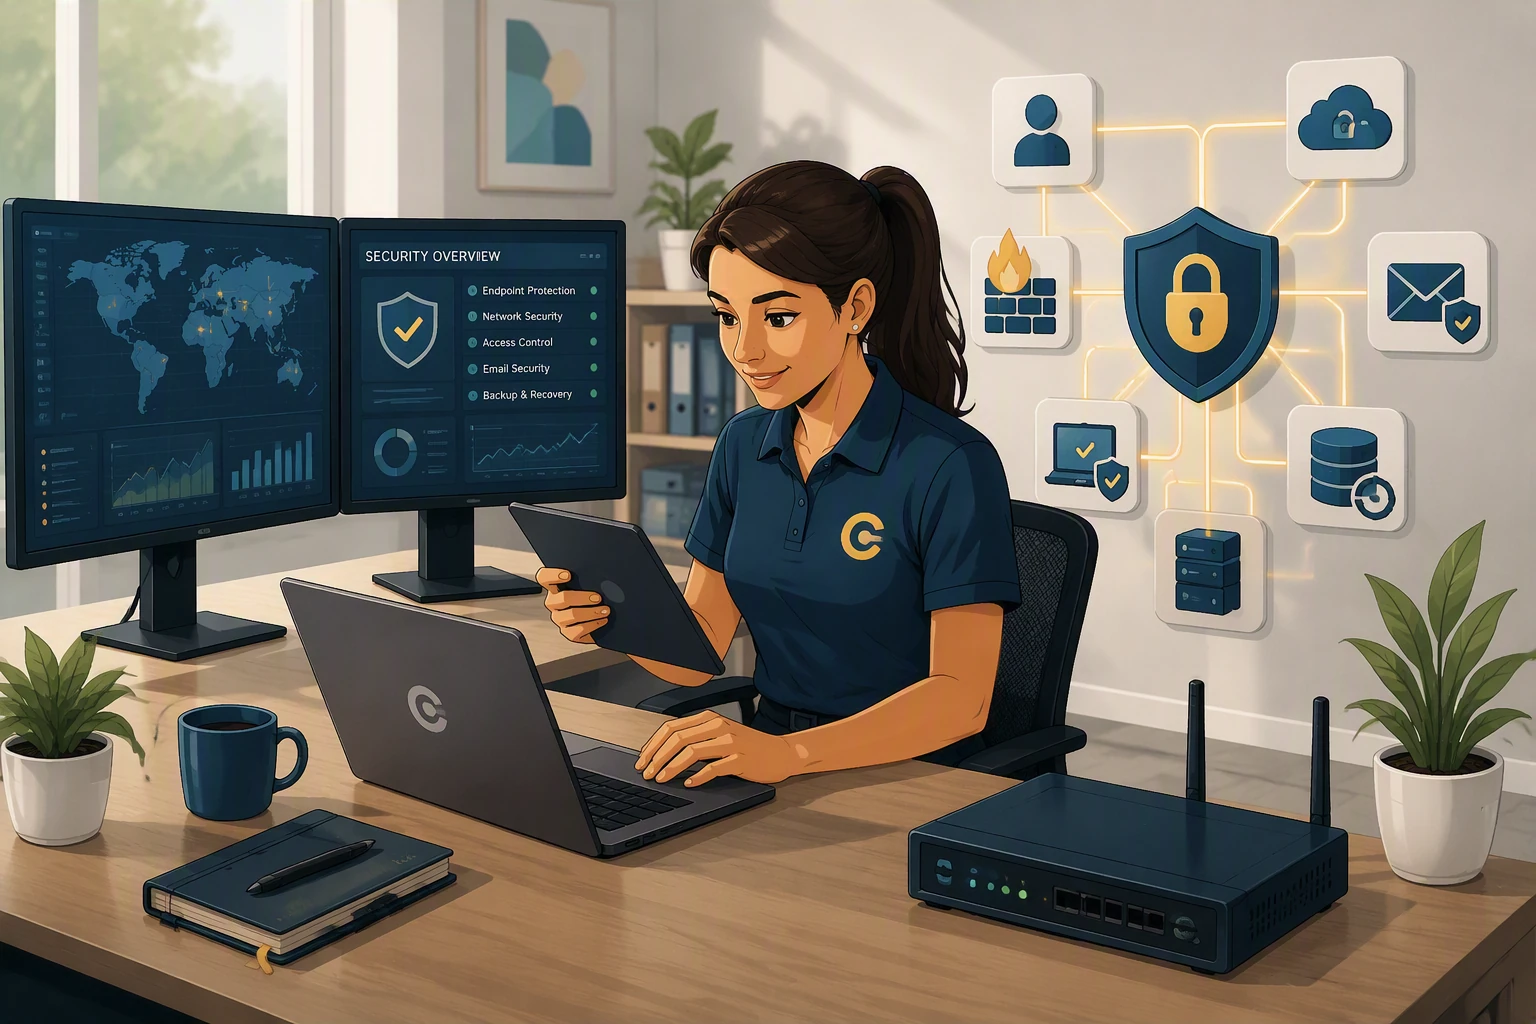
What the service brings together
Shaped by the ASD Essential Eight (AU), the NIST Cybersecurity Framework (US) and the principles behind ISO 27001 and GDPR (EU) — used to prioritise, not just to tick a box.
Multi-factor authentication, conditional access and least-privilege permissions configured properly across Microsoft 365 and critical systems.
Priority patching and application control matched to Essential Eight maturity guidance, reducing the window an attacker has to exploit.
Ongoing monitoring across identity, endpoint and cloud so early signs of compromise are caught, not discovered by the business.
Recovery plans and backups tested to actually restore, not just configured once and left.
Plain-English risk reporting and follow-through on remediation — the extra step most providers skip once the assessment is delivered.
Controls implemented properly
We select and configure security platforms around your actual risk rather than a generic template, then keep them maintained — not just switched on once and left.
A framework drawn from AU, US and EU practice
Rather than inventing our own checklist, we apply the five functions at the core of the US NIST Cybersecurity Framework, cross-checked against Essential Eight priorities (AU) and ISO 27001/GDPR-grade data discipline (EU) — then go further with the reporting most providers skip.
Map assets, data and risk across the environment, so priorities are based on what actually matters to the business.
Harden identity, endpoints, email and access before an incident happens, not after.
Monitor for the early signs of compromise, rather than waiting for something to break.
Follow a clear, practised plan when something goes wrong, not improvisation under pressure.
Restore from backups that are actually tested to work, and confirm the business is genuinely back to normal.
Plain-English reporting on posture and risk, with a follow-up roadmap — the extra mile most providers stop short of.
Communication and documentation
We explain what we found, why it matters and what we recommend — not a compliance report full of jargon nobody reads.
Security baselines, remediation priorities, control coverage and improvement roadmaps are documented so your security posture stays understandable, defensible and ready for the next review.
Looking for a partner that goes beyond the compliance minimum?
Free technology and security assessment
We will review your technology, security, Microsoft 365 environment, communications and AI readiness, then provide clear, practical recommendations.